 My Beast
Discounts and news by email. Unsubscribe in one click.
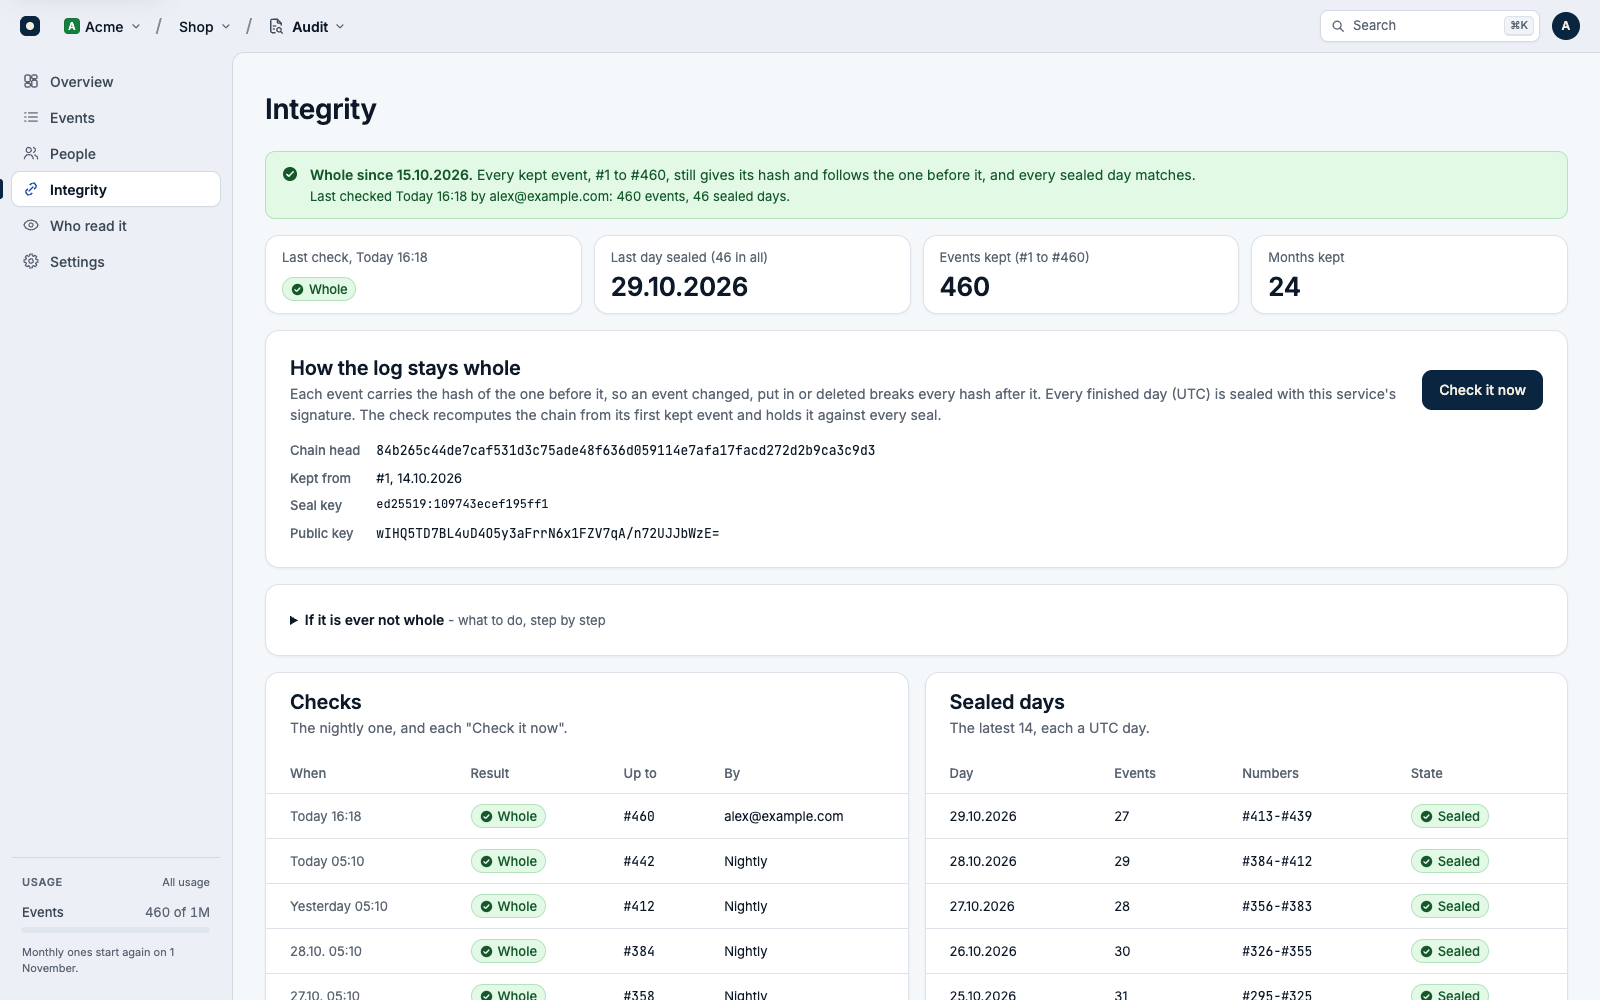
Your app records who did what, to what and about whom, in the same transaction as the action. Each project's events form a hash chain, each finished day is sealed with a signed checkpoint, and a daily check names the first event that does not match. Reading the log is recorded too.
For security and developers.
You sign up and pay for Audit separately from hosting.
Prices are without VAT: VAT is added at checkout, where it applies. Plans renew each month or year until you cancel. Ask within 30 days of your first payment, or 14 days of a renewal, and you get it back in full. Sold by our reseller Paddle, which handles payment, VAT and invoices. Terms · Refunds
Pick Audit and a plan, name your project and pay.
Install the Laravel package, run its migration for the outbox, and put the address and a server secret in .env.
Call Audit::record() where your app acts: who did it, to what, about whom and why. The scheduler sends them every minute.
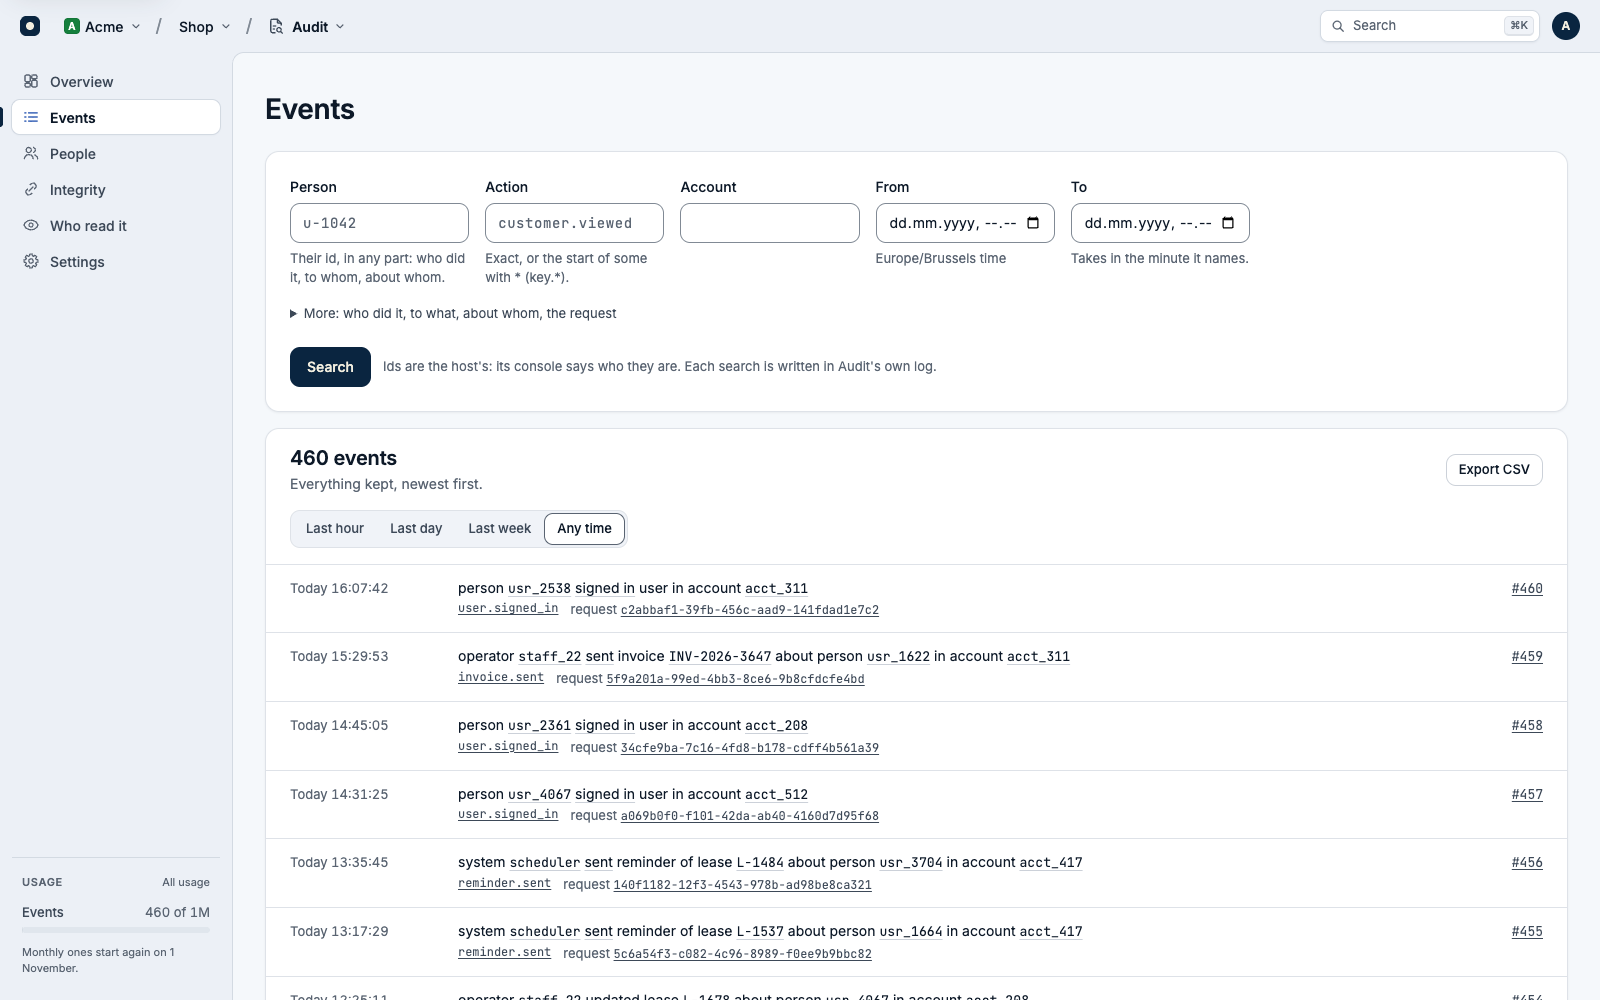
Find events by person, action or time, open a person's access report, and see on the Integrity page that the log is whole.
| Starter€9 a month€90 a year | Team€49 a month€490 a year | Business€149 a month€1,490 a year | |
|---|---|---|---|
| Events kept for | 3 months | 6 months | 24 months |
| Events a month | 100,000 events | 1,000,000 events | 10,000,000 events |
Events past the plan's monthly number are still kept and counted, never turned away.
mybeast/audit-laravelEvents are only ever added, in a hash chain per project, and each finished day is sealed with a signed checkpoint, so a change shows. An event with an email address in it is refused. Every search, event opened and export is recorded, in a chain of its own.
Audit never turns an event away. Past the plan's monthly number, events are still kept, counted and shown as over. How long events are kept can be set up to the plan's most; moving to a smaller plan brings that down, and older events then go.
There is no free plan. In your tests, Audit::fake() keeps events in memory and sends nothing, and MYBEAST_AUDIT_ENABLED=false checks events without writing them.
The SDK is for Laravel 12 and 13 on PHP 8.2 or later. Any other app can send events to the HTTP API with a server secret, in batches of up to 500, but it has to keep its own outbox.
On our servers in Germany. Events are kept for the months set in the project's settings, at most 3, 6 or 24 months, by plan; then whole sealed days are removed. The record of who read the log is kept for 24 months.
Events are only ever added. Each carries the hash of the one before, and each finished day is sealed with a signed checkpoint. A check once a day, or one you start on the Integrity page, names the first event that does not match.
Only what your app sends: ids for who acted, the target, and the person and account an event is about, with the action, the time, a reason and some context. An event with an email address in it is refused.
Events wait in the outbox in your database and are sent, oldest first, when it is back. Nothing is lost.